Hire a virtual IT department.
Role-specialised AI agents for the service desk, security operations, systems and networks. Your people lead them and approve every change, and a tamper-evident ledger records who did what.
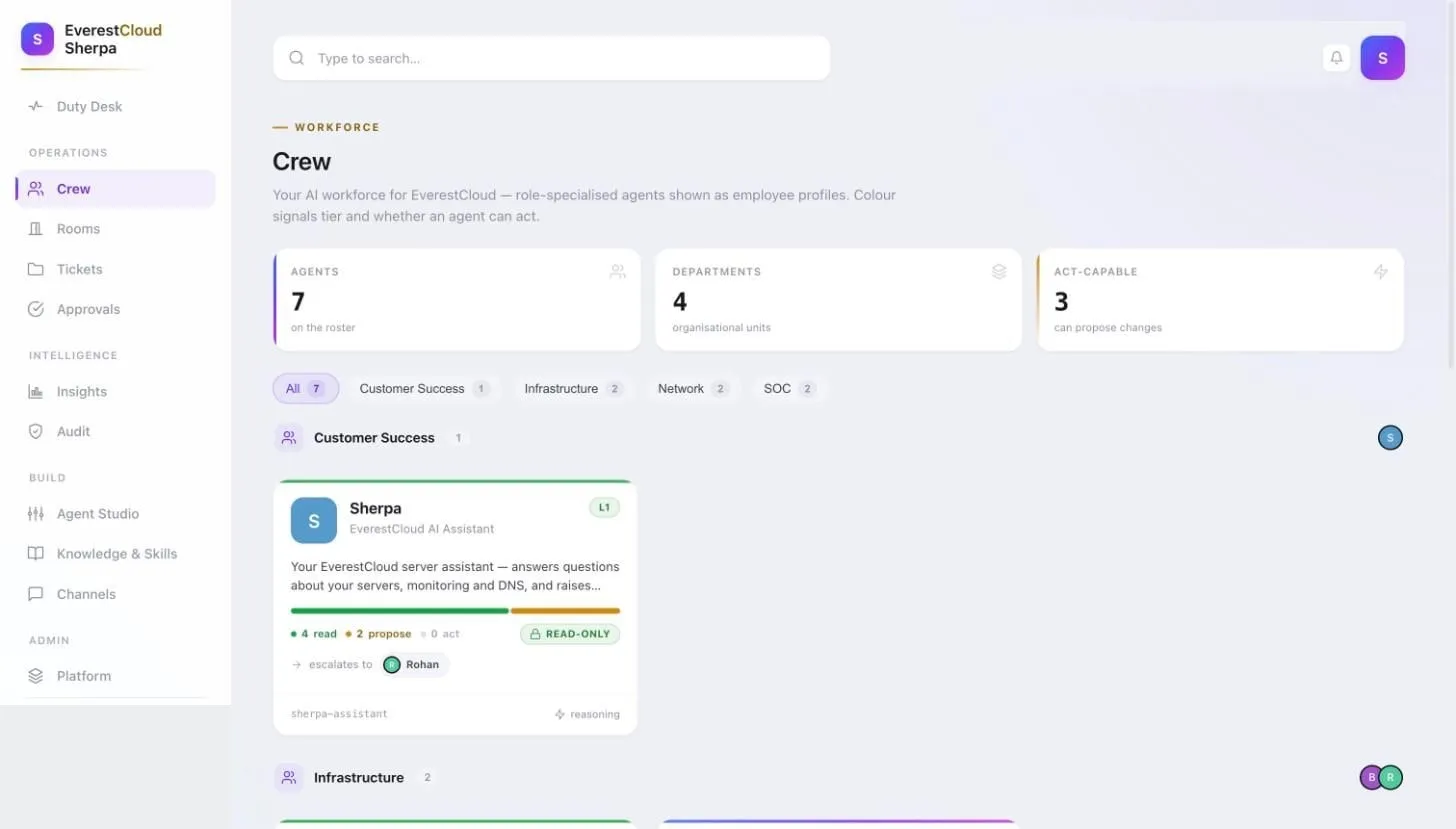
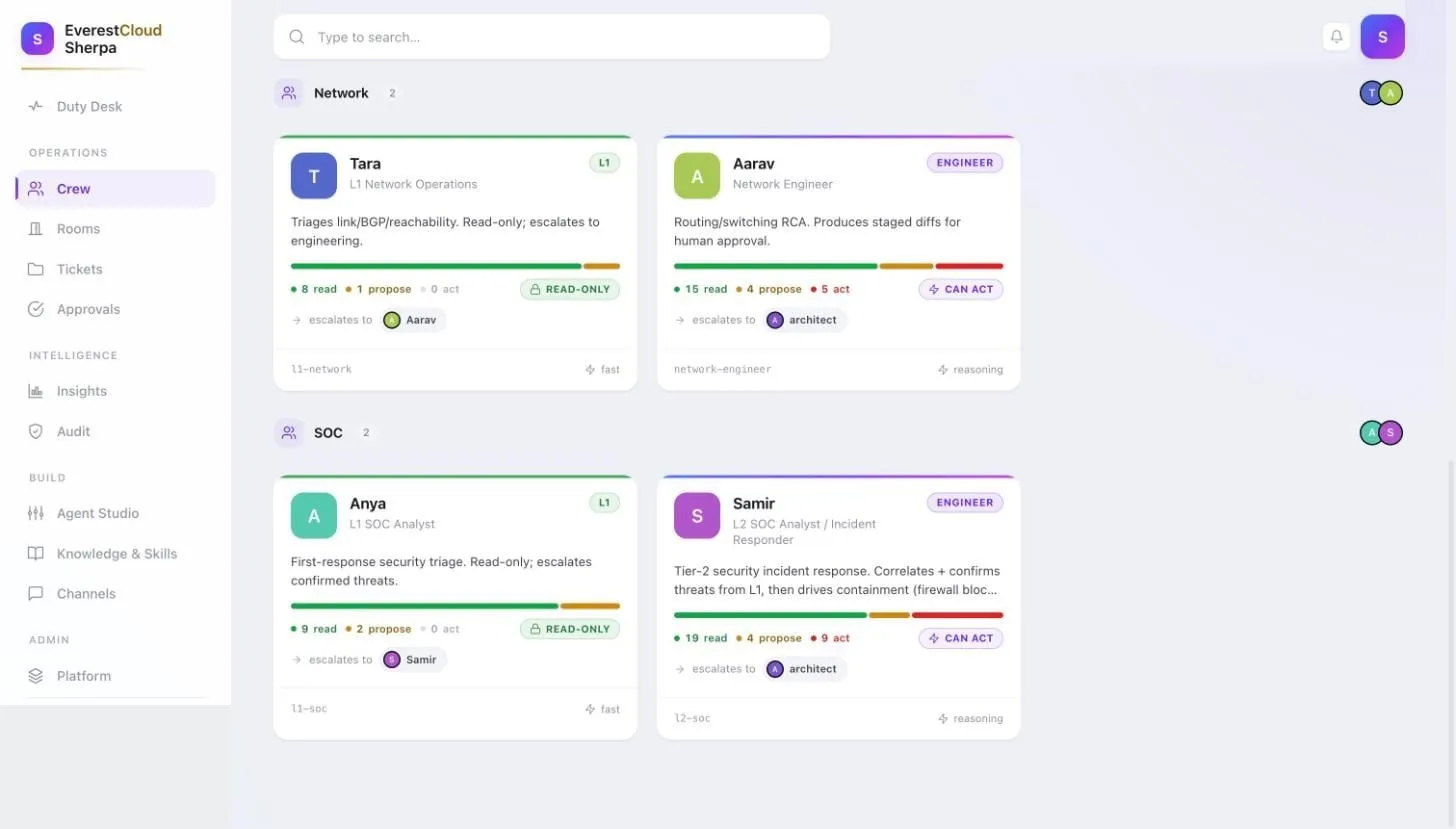
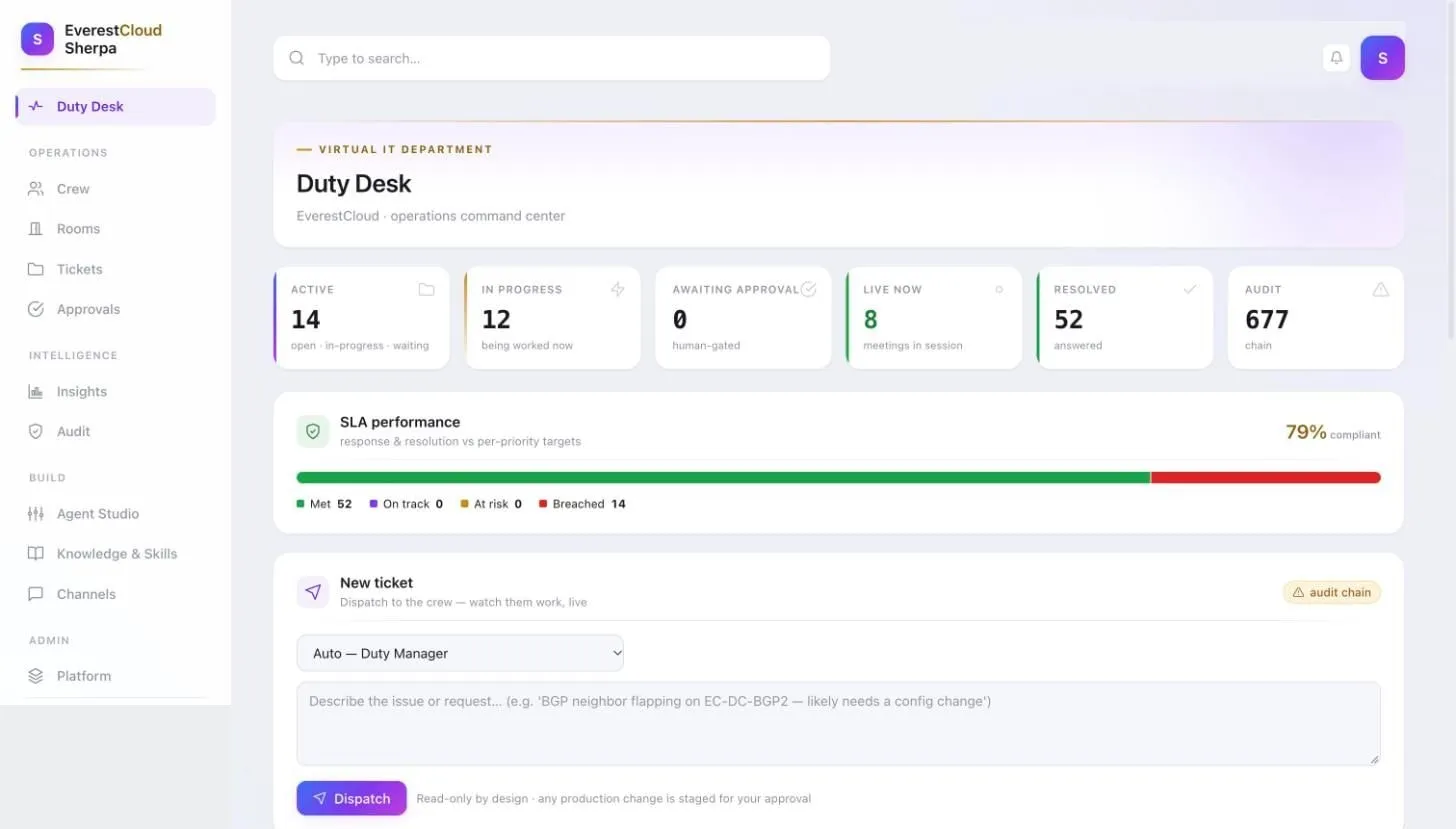
- roles, from the service desk to the network engineer
- A crew of 7
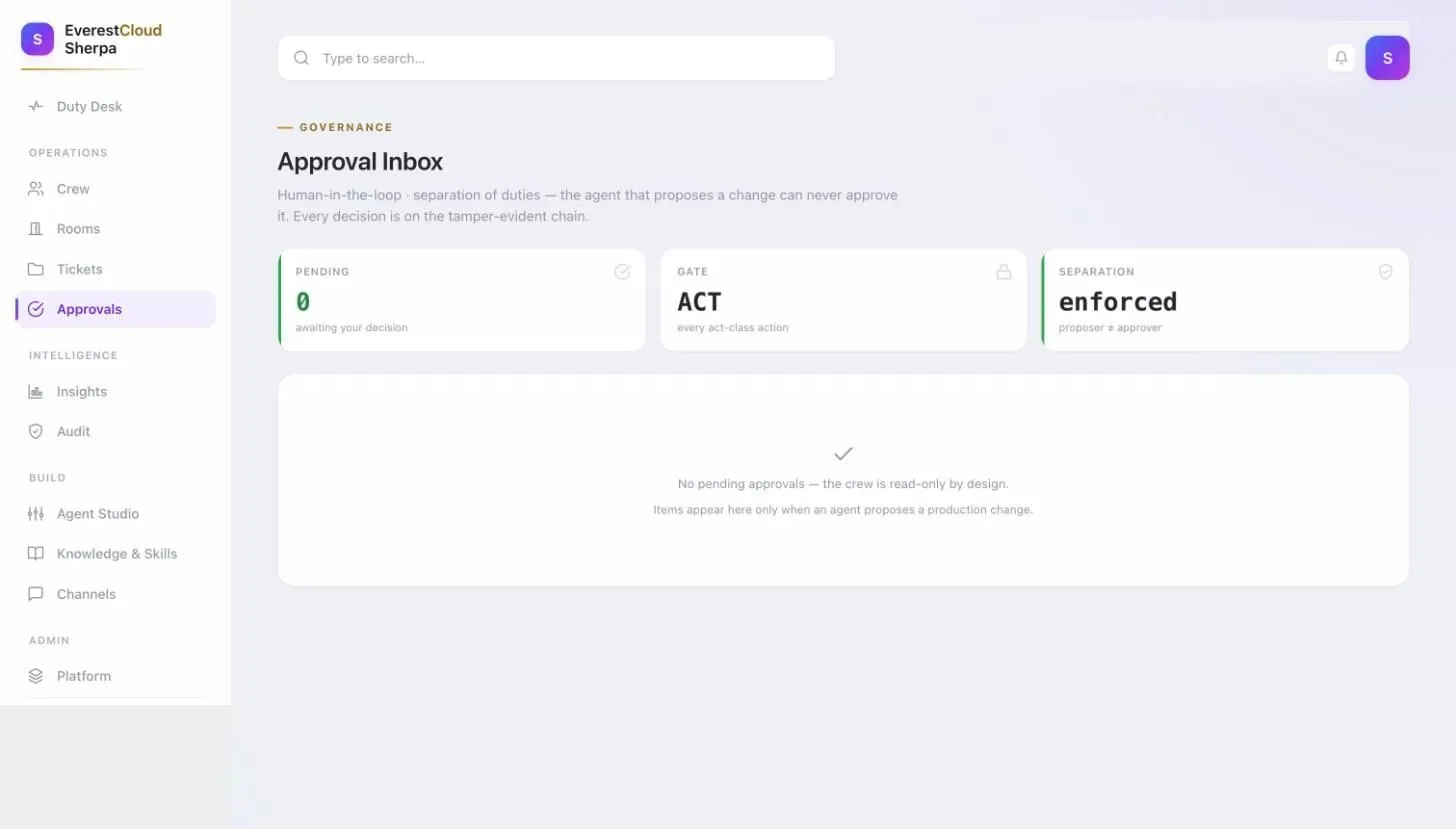
- of changes before any of them runs
- A person approves 100%
- isolated crew, knowledge base and ledger
- Per organisation 1
- June, inside EverestCloud's portal
- In production since 2026
The crew
Seven roles today
Each role reads from your systems, triages and proposes. None of them changes anything without a person.
-
Service-desk assistant
Answers customers about their own servers from your knowledge base, and raises change requests.
-
L1 SOC analyst
Triages security alerts and proposes a block for a person to approve.
-
L2 SOC analyst
Takes what L1 escalates, investigates across your logs and alerts, and proposes the response.
-
L1 system operator
First-line checks and triage on servers and platform. Reads, never changes.
-
L1 network operator
First-line checks and triage on the network. Reads, never changes.
-
System engineer
Day-2 health, capacity and root cause. Changes are staged and run only after an approval.
-
Network engineer
Routing, switching and firewall root cause. Configuration changes are staged and run only after an approval.
How a request moves
From a question to a recorded change
- 01
Someone asks
From the portal widget, the console, Slack or Microsoft Teams.
- 02
The duty manager routes it
To the right role, or to several roles at once.
- 03
The role reads and proposes
It reads from your systems and answers, or proposes a change.
- 04
A person approves
Nothing changes until someone on your staff approves it.
- 05
The change runs and is recorded
Who asked, who proposed, who approved and what ran, all on the ledger.
A cross-domain incident fans out to several roles at once and comes back as one root-cause analysis.
Why you can trust it
Approval gates by construction, not by policy
-
The L1 roles cannot act at all
They read, triage and propose. Engineers act only through an approval. There is no setting that turns this off.
-
A hash-chained audit ledger
Every action is appended to a tamper-evident ledger, with a verify endpoint so your auditors can check it themselves.
-
One isolated crew per organisation
Each organisation gets its own crew, knowledge base and ledger. The system fails closed.
-
Memory and cost you can see
Per-organisation memory and cost insight, so you know what the crew remembers and what it spends.
Connects to what you run
Your monitoring, your inventory, your network, your chat
-
Reads from
- Zabbix
- NetBox
- Prometheus
- OpenSearch
- Any REST API
-
Gated actions on
- Nutanix
- Cisco Firepower
- DNS
- Authentik
- Zabbix
-
Works from
- Slack
- Microsoft Teams
- The portal widget
- The console
Proof
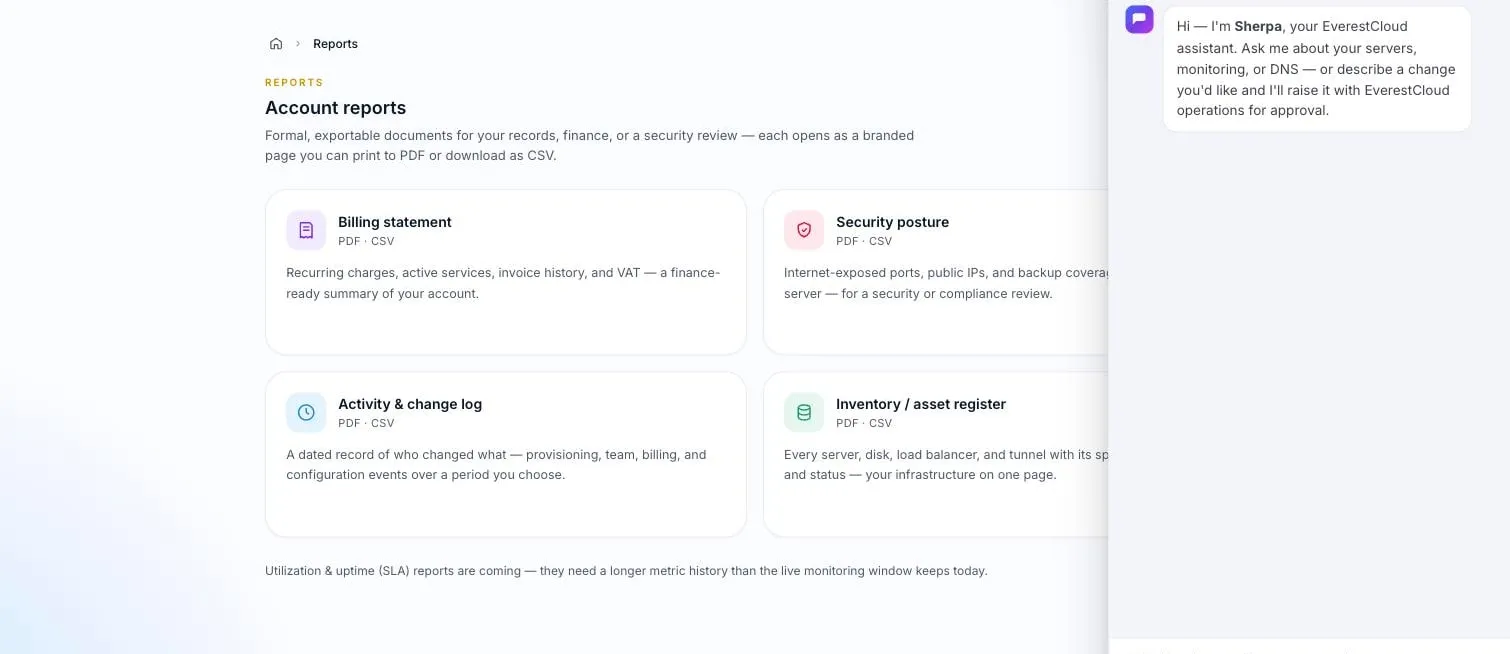
In production since June 2026
The customer assistant has answered inside EverestCloud's portal since June 2026, scoped to each customer's own servers and metrics.
Deployment
Runs where your data is
-
Self-hosted
On your premises, or air-gapped.
The model is pluggable, from a frontier API to a local GPU in your own data centre.
For MSPs
White-label, one crew per customer
Resell Altiport Crew under your own brand, with one isolated crew, knowledge base and ledger per customer.
Book a Crew demo
Watch the crew work a real request, from the question to the approval to the ledger entry.
Book a Crew demo